
SOC Services
Your security environment. Monitored around the clock.
Seraph's Security Operations Centre combines analyst expertise with threat intelligence to detect, investigate and respond to incidents across your environment — day and night.
- 24/7
Monitoring - Threat Detection
& Response - Escalation
Workflows
- MonitoringActive
- Coverage Window24 / 7 / 365
- Escalation PathDefined per agreement
- Current TierConfigurable
Threat activity (last 24 hours)
Global threat landscape
Recent security events
View all events →- HighSuspicious authentication attemptLondon, UK2 minutes ago
- MediumUnusual data access patternSingapore18 minutes ago
- LowNew asset onboardedAWS1 hour ago
- LowPolicy change detectedInternal3 hours ago
Sample data
Most teams can't watch everything, all the time.
Security tools generate more signal than any internal team can consistently review — and attackers know it.
Alert Fatigue
Disconnected tools generate more alerts than any internal team can realistically triage.
Limited Visibility
Blind spots across endpoints, identity, cloud and network make incidents harder to catch early.
No 24/7 Coverage
Attacks don't wait for business hours, but most internal teams cannot staff around the clock.
Inconsistent Response
Without a defined workflow, incident handling varies by who happens to be available.
What the SOC does,
end to end.
From first alert to lessons learned, the SOC covers the full lifecycle of monitoring and response.
Need coverage we haven't listed?
Every SOC engagement is tailored to your environment. Tell us what you need and we'll show you how it's covered.
Talk to our SOC teamConnects to your environment.
Data sources are onboarded by category. Coverage within a category depends on the specific product and configuration in your environment.
Identity
AvailableAuthentication and identity provider signals.
Endpoint
AvailableEndpoint detection and response telemetry.
Email security and gateway telemetry.
Cloud
AvailableCloud platform and workload activity logs.
Network
AvailableNetwork and perimeter security telemetry.
SIEM / Log Sources
AvailableAggregated logs from an existing SIEM or log platform.
Standards & Frameworks
Relevant Standards &
Frameworks
SOC processes are informed by established industry frameworks for detection and incident handling.
How the SOC connects to your environment.
A straightforward data path from your environment to a validated response — with an analyst in the loop at every stage.
Your Environment
Endpoints, identity, network, cloud and email.
Data Collection
Telemetry and logs are collected from connected sources.
Seraph SOC
Detection logic and intelligence enrichment are applied.
Analysts
Alerts are triaged, investigated and escalated by analysts.
Customer
You receive validated alerts, guidance and status reporting.
TelemetryAlertValidated
Incident Workflow
From detection to
lessons learned.
A consistent workflow governs every incident, regardless of severity — so response is predictable rather than improvised.
- 01
Triage
01 – 03- DetectAn alert is generated from monitored telemetry.
- ValidateAnalysts confirm the alert is not a false positive.
- InvestigateScope, cause and affected assets are established.
- 02
Decide
04 – 05- PrioritizeSeverity is assigned based on impact and confidence.
- EscalateValidated incidents are escalated to your team.
- 03
Act
06 – 08- RespondAgreed containment and response actions are taken.
- RecoverAffected systems are restored to normal operation.
- LearnThe incident is reviewed to improve future detection.
Severity that reflects real impact.
Every incident is classified consistently, so priority and escalation are never a judgment call made under pressure.
- P1
Critical
Active compromise or imminent, severe business impact. Immediate escalation.
- P2
High
Significant risk to systems or data requiring urgent attention.
- P3
Medium
Confirmed issue with limited scope or contained impact.
- P4
Informational
Notable activity for awareness, not requiring immediate action.
Service levels, agreed in writing.
Specific commitments for each category below are defined per service agreement and scaled to your selected tier — not published as generic figures here.
Alert Acknowledgement
Per AgreementTime to first analyst acknowledgement of a generated alert.
Incident Escalation
Per AgreementTime to escalate a validated incident to your team.
Status Reporting
Per AgreementFrequency and format of SOC status and activity reporting.
Change Requests
Per AgreementTurnaround for detection rule or monitoring scope changes.
Visibility into what the SOC is doing.
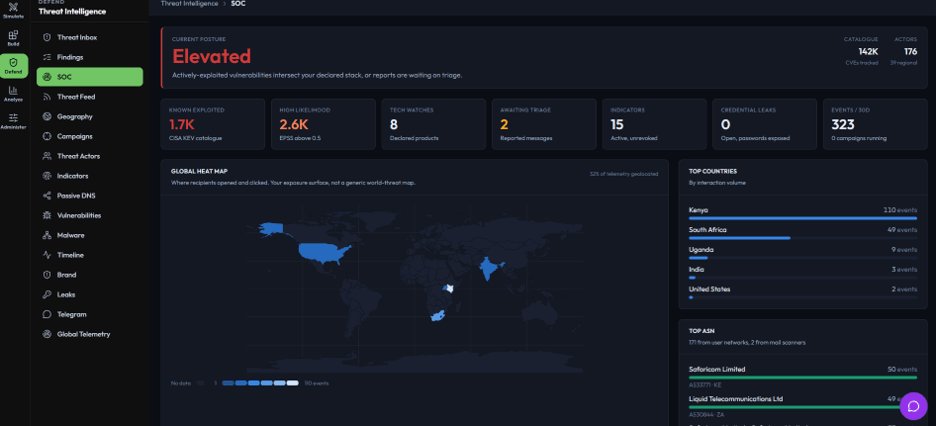
Customers receive regular reporting on SOC activity — alert volume, incident trends and status against agreed service levels — delivered from the same exposure dashboard shown here.
- — Scheduled activity and trend reporting
- — Incident summaries with root cause and actions taken
- — On-demand reporting for audit or compliance needs
Alerts backed by intelligence, not just logs.
Seraph's threat intelligence connects raw signals to known threat actors, indicators and context — so escalations arrive with meaning attached.
Threat Actor
Regional and global threat intelligence inform detection priorities.
IOC
Indicators are linked to known threat actor behavior where possible.
Alert
Enrichment happens before an alert reaches your team, not after.
Affected Asset
Incident
Intelligence context helps distinguish targeted activity from noise.
Response
Choose the model that fits your team.
Every tier follows the same workflow and severity model — the difference is coverage, response involvement and reporting depth. Speak to our team for tier-specific commercials.
Essential
Core monitoring and alerting for teams building out their security operations.
- Continuous monitoring of onboarded sources
- Alert triage and validation
- Incident escalation to your team
- Scheduled activity reporting
Advanced
Deeper investigation support and more active involvement in response.
- Everything in Essential
- Guided incident investigation
- Threat intelligence enrichment on escalated alerts
- Detection tuning for your environment
Enterprise
The highest level of SOC involvement, for organizations with complex environments.
- Everything in Advanced
- Analyst-guided response coordination
- Custom detection engineering
- Dedicated reporting cadence
Frequently Asked Questions
Can't find what you need? Ask a security expert.
Ready for continuous monitoring and response?
Tell us about your environment and current coverage. Our team will help determine the right SOC engagement for you.