
Secure the infrastructure everything else depends on.
Seraph Cyber designs, implements and secures the core infrastructure organizations depend on to protect users, systems and business operations. We support organizations in deploying secure network controls, identity infrastructure and remote-access technologies based on security best practices and business requirements.
Core infrastructure is a primary target, not a background concern.
Firewalls, identity systems and remote access are foundational controls — when misconfigured or left unreviewed, they become the easiest way in.
Misconfigured Perimeter Controls
Firewalls and network segmentation that aren't properly configured leave critical systems exposed to lateral movement and external attack.
Weak Identity Infrastructure
Active Directory environments without proper hardening and privileged access controls are a primary target for credential-based attacks.
Insecure Remote Access
VPN and remote-access solutions deployed without strong security controls can become an entry point rather than a safeguard.
Configuration Drift Over Time
Network and identity security controls that aren't periodically reviewed accumulate unnecessary exposure as environments change.
Everything needed to secure your core infrastructure.
Secure network controls, identity infrastructure and remote-access technologies, built on security best practices and your business requirements.
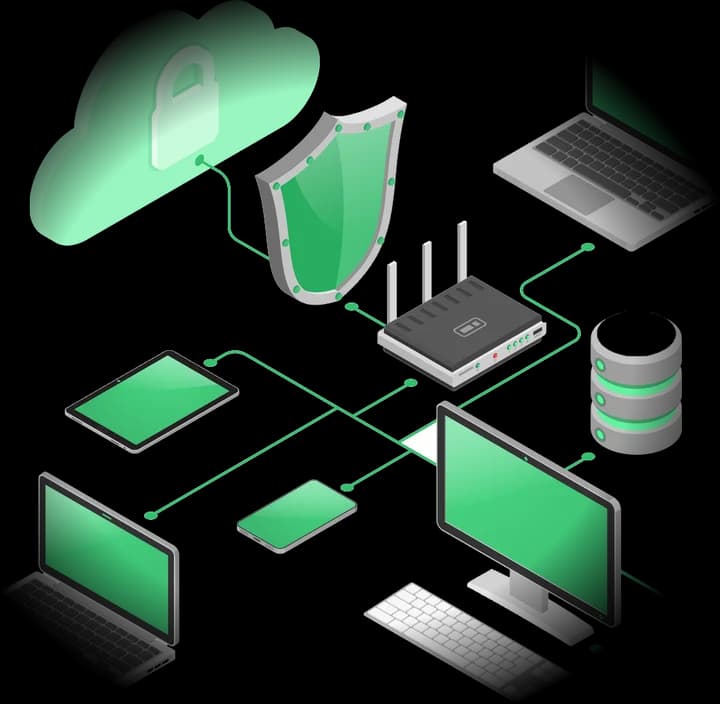
Firewall Deployment & Configuration
Installation, configuration and hardening of next-generation firewalls, including security policies, network segmentation, NAT, intrusion prevention, application control, web filtering and secure traffic management.
Active Directory & Identity Infrastructure
Design, deployment, configuration and security hardening of Microsoft Active Directory environments, including domain architecture, Group Policy, user and computer management, privileged access controls and integration with Microsoft Entra ID where required.
VPN & Secure Remote Access
Implementation of secure site-to-site and remote-access VPN solutions to protect communication between offices, cloud environments, employees and business systems.
Network Security Architecture
Design and review of secure network architectures incorporating segmentation, VLANs, DMZs, access controls and appropriate security zones.
Infrastructure Security Hardening
Security configuration and hardening of servers, network devices and supporting infrastructure to reduce attack surfaces and strengthen resilience.
Configuration Review & Optimization
Periodic assessment of firewall rules, VPN configurations, Active Directory controls and network-security configurations to identify weaknesses and unnecessary exposure.
A structured approach to securing core infrastructure.
Every engagement follows the same disciplined process, tailored to your environment and requirements.
- 01
Discovery & Requirements
Current network, identity and remote-access infrastructure is reviewed against business and security requirements.
- 02
Design & Architecture
Secure network, identity and remote-access architecture is designed to match your environment and risk profile.
- 03
Implementation & Configuration
Firewalls, identity infrastructure and remote-access solutions are deployed and configured according to security best practices.
- 04
Hardening
Servers, network devices and supporting infrastructure are hardened to reduce attack surface.
- 05
Validation
Configurations are reviewed and tested to confirm controls are working as intended.
- 06
Ongoing Review
Firewall rules, VPN configurations and identity controls are periodically reassessed to close emerging gaps.
Relevant Standards & Frameworks
Deployments and reviews are structured around recognized security frameworks and vendor best practices, selected to match your environment.
Infrastructure you can operate with confidence.
Every engagement is delivered with clear documentation and configuration evidence, not just a completed task.
- Architecture & Configuration DocumentationDocumented network, identity and remote-access architecture and configuration decisions.
- Hardening & Configuration ReportA record of security configurations applied across firewalls, identity infrastructure and supporting systems.
- Configuration Review FindingsFindings and recommendations from firewall, VPN and Active Directory configuration reviews.
- Remediation GuidancePractical, prioritized guidance for addressing identified weaknesses and exposure.
Why Seraph.
Threat-Informed
Current threat and vulnerability intelligence adds context to assessments and recommendations.
Business-Focused
Technical findings are connected to their potential impact on the organization.
Expert-Led
Engagements are delivered by cybersecurity practitioners with specialist expertise.
Actionable
Every engagement results in clear recommendations, priorities and next steps.
Frequently Asked Questions
Can't find what you need? Ask a security expert.
Ready to secure your core infrastructure?
Tell us about your network, identity and remote-access environment. Our team will help scope the right engagement.